
Juniper Networks SSG 300 series is a range of high-performance security platforms that can block attacks, prevent unauthorized access, and comply with cybersecurity regulations. It supports various UTM security protection functions, including antivirus, anti-spyware, and anti-phishing. It also features security zone configuration, virtual routers, and virtual LANs, allowing network segmentation and application of different security policies. Additionally, it supports a variety of I/O interface options and WAN protocols, making it suitable for deployment as a branch router or integrated security and routing device.
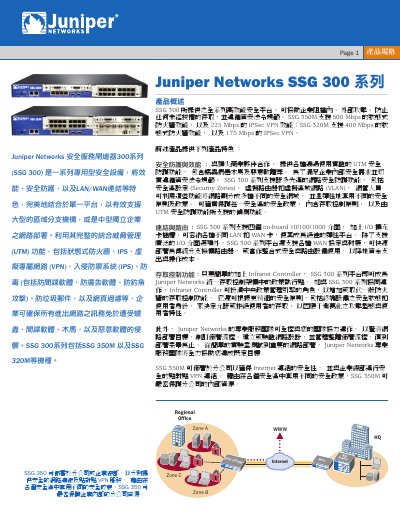
The Juniper Networks SSG 300 Series provides a high-performance security platform designed to help enterprises block internal and external attacks and prevent unauthorized access. The series includes the SSG 320M and SSG 350M models, which support various UTM security features such as antivirus, anti-spam, web filtering, and IPS. This manual is written in Chinese.
| Stateful Firewall Performance (SSG 350M) | 500 Mbps |
|---|---|
| IPSec VPN Performance (SSG 350M) | 225 Mbps |
| Stateful Firewall Performance (SSG 320M) | 400 Mbps |
| IPSec VPN Performance (SSG 320M) | 175 Mbps |
| Fixed Interfaces | 4x 10/100/1000 |
| RAM (All Models) | 1GB |
| DRAM (SSG 320M/350M) | 256MB |
| IPS Performance (SSG 350M) | 200,000+ |
| IPSec VPN Sessions (SSG 350M) | 350 |
Yes, with the addition of Infranet Controller, the platform can serve as a policy enforcement point in the Juniper Networks Unified Access Control architecture.
The platform supports various WAN protocols including T1, E1, Serial, ADSL/ADSL2/ADSL2+, G.SHDSL, DS3, E3, 10/100/1000, and SFP.
The routing engine supports OSPF, BGP, and RIP v1/2, and is compatible with Frame Relay, Multilink Frame Relay, PPP, Multilink PPP, and HDLC.