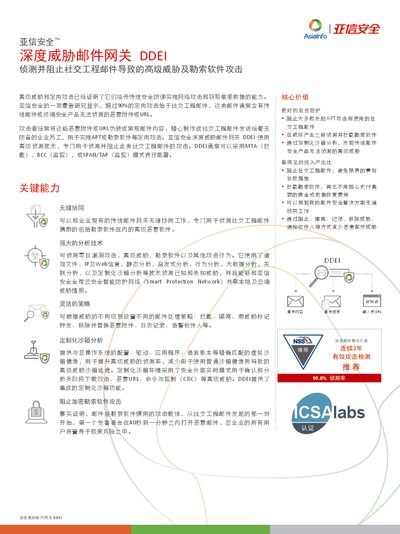
The Asiainfo Security DDEI series (7100, 9100, 5100) is a deep‑threat email gateway that detects and blocks advanced social‑engineering and ransomware attacks.
About this manual
The DDEI deep‑threat email gateway uses advanced detection technologies—including file, IP and web reputation, static and heuristic analysis, behavior analysis, big‑data correlation, and custom sandbox analysis—to identify known and unknown threats in social‑engineering emails. It can be deployed in MTA (blocking), BCC (monitoring) or SPAN/TAP (monitoring) modes and works seamlessly with existing enterprise mail gateways.
Technical specifications include processing capacities of up to 400,000 emails/day for the DDEI 7100, 800,000 emails/day for the DDEI 9100, and 100,000 emails/day for the DDEI 5100, with redundant power supplies (550 W for 1U models, 750 W for 2U models) and rack‑mount designs. The solution integrates with Asiainfo’s Deep Discovery platform and can share threat intelligence with the global Smart Protection Network. This manual is written in Chinese.
What's inside
- Core Value
- Key Capabilities
- Technical Specifications
- Deployment Options
- Email Policies
- Custom Sandbox Analysis
- Deep Threat Discovery Platform
Specifications
| Processing capacity (DDEI 7100) | 400,000 emails/day |
|---|
| Processing capacity (DDEI 9100) | 800,000 emails/day |
|---|
| Processing capacity (DDEI 5100) | 100,000 emails/day |
|---|
| Power supply (DDEI 7100 / 5100) | 550W redundant, 1U rack design |
|---|
Frequently asked questions
What deployment modes does DDEI support?
DDEI can be deployed in MTA (blocking), BCC (monitoring), or SPAN/TAP (monitoring) modes.
How does DDEI detect ransomware?
It uses signature and reputation analysis, communication fingerprinting, script simulation, zero‑day analysis, and custom sandbox analysis to detect both known and unknown ransomware.
Can DDEI work with existing email gateways?
Yes, DDEI can seamlessly cooperate with an enterprise’s existing traditional email gateway.